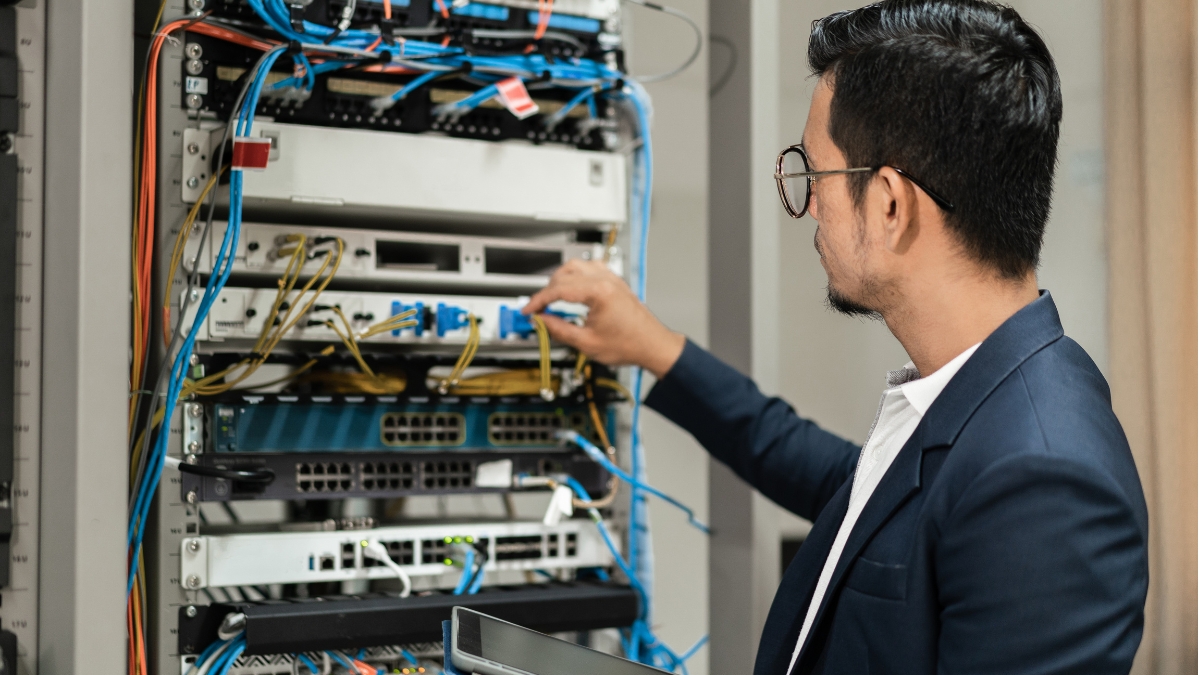
Network infrastructure standardization helps reduce cyber risk by establishing consistent security configurations, patching processes, and change controls across locations.It gives IT and security teams a repeatable way to manage vulnerabilities and maintain approved configurations as the business grows.
Your locations can have different footprints. They should not have different definitions of secure.
At Federated Service Solutions, we connect network design, technology deployment, and ongoing support to help multi-site businesses put consistent infrastructure into practice.
What Is Network Infrastructure Standardization?
Network infrastructure standardization means establishing approved equipment, configuration baselines, and operating procedures across your locations. A configuration baseline documents agreed settings and provides the reference point for controlled changes.
That does not mean forcing a warehouse and a small office into identical designs. Standardize security requirements, then document approved differences for capacity, layout, and business needs.
- For Leadership, make those standards part of investment planning
- For IT, define supported hardware and repeatable support procedures
- For Security teams, establish the controls every location must meet
- For Operations, plan upgrades around business hours and critical workflows
The goal is shared accountability, not another document nobody follows.
How Does Standardization Reduce Cyber Risk?
It closes configuration gaps
One location should not allow unrestricted remote administration while another tightly controls it. Establish approved settings for firewall rules, management access, and unnecessary services. Store configurations centrally and investigate changes outside the approved change-management process, practices recommended by the Cybersecurity and Infrastructure Security Agency (CISA).
Security should follow a documented standard, not depend on who configured the last device.
Standardize access policies, not passwords. Require individual administrative accounts, appropriate privileges, and multifactor authentication wherever supported. Never use a shared local administrator password as a shortcut for nationwide deployment.
It makes patching more manageable
Treat patching as an enterprise process rather than a collection of local tasks. Identify affected equipment, prioritize updates, test deployment, and verify installation.
The National Institute of Standards and Technology (NIST) describes patching as preventive maintenance that helps prevent compromises, data breaches, and operational disruption.
An approved equipment portfolio gives teams fewer unnecessary variations to account for when planning that work.
It limits unnecessary access between systems
Apply consistent segmentation policies to separate corporate systems, guest Wi-Fi, payment devices, and connected equipment. Permit only the communication each system requires.
Properly enforced segmentation can restrict an attacker’s movement after an initial compromise. Creating separate network segments is only part of the job; access controls must enforce the boundaries between them.
It makes configuration drift easier to address
A secure installation is not the finish line. Settings can change during troubleshooting, upgrades, and everyday maintenance. Compare deployed configurations against the approved baseline, review exceptions, and assign responsibility for corrections.
Document who approved each exception, why it exists, and when it must be reviewed. A temporary workaround should not quietly become the permanent network design.
How Do You Standardize Networks Nationwide?
Start with visibility, not a shopping list
Build a site-by-site inventory of equipment, firmware, connectivity, and business requirements. Identify unsupported devices, inconsistent configurations, and undocumented exceptions before deciding what to replace.
Look beyond the hardware model. Record support status, device ownership, administrative access, and dependencies such as payment processing or warehouse applications. Prioritize remediation by risk and operational impact, rather than upgrading whichever location happens to complain first.
Use those findings to establish an approved design and prioritize rollout phases. Bring IT, security, and operations into planning so technical requirements and operating schedules are addressed together.
Validate the standard before scaling it
A faulty template can repeat the same mistake across multiple sites. Pilot the design at representative locations, test required application traffic and security controls, and establish a rollback plan before expanding.
Define acceptance criteria before deployment. Require configuration records, test results, and documented exceptions at closeout. “Installed” should not be the only measure of success.
Coordinate equipment delivery, technician access, maintenance windows, and escalation contacts before each cutover. Assign someone to approve the return to service, and confirm that site managers know where to report problems.
FSS supports execution through equipment procurement, staging and configuration, structured cabling, installation, testing, and coordinated cutovers. Our teams work across all 50 states, Canada, Puerto Rico, and Guam, adapting quickly as schedules and requirements change.
Keep the standard alive after deployment
Include ownership, configuration reviews, and update procedures in the operating plan, not just the project plan.
FSS’ ongoing network management, Help Desk, and on-site support extend the relationship beyond installation. As locations open, equipment changes, and priorities shift, your team has a partner supporting the infrastructure throughout its lifecycle.
Track progress through practical measures: locations meeting the approved baseline, overdue updates, unsupported devices, and unresolved exceptions. Use those measures to focus the next round of work.
Set targets, name an owner for each metric, and review trends regularly. A deployment completion report tells you what was installed. Ongoing reporting should show whether the agreed standards are still being maintained.
Network Infrastructure Standardization FAQs
Does standardization mean every site must be identical?
No. Establish shared security requirements, then tailor each site’s design to its operational needs. Document approved differences and manage subsequent changes against the applicable baseline.
Does standardizing network infrastructure eliminate cyber risk?
No. Standardization supports cybersecurity, but shared configurations still require testing, timely updates, access controls, and ongoing monitoring. Consistency is valuable only when the underlying standards remain secure and current.
Can businesses standardize networks without replacing everything?
Yes, when existing equipment remains supported and meets your security requirements. Start with an assessment, retain suitable assets, address configuration gaps, and phase replacements according to risk, compatibility, and operational needs.
Make Consistency Part of Your Security Strategy
Your security standards should not stop where headquarters ends.
Federated Service Solutions brings network design, nationwide deployment, and long-term support together to help your business turn infrastructure plans into consistent execution.
Contact FSS to discuss standardizing network infrastructure across your locations.